NDR for Firebox
Behavioral detection and response based on network activity, VPN, and DHCP telemetry from supported Fireboxes.
 Start a conversation
The network intelligence layer
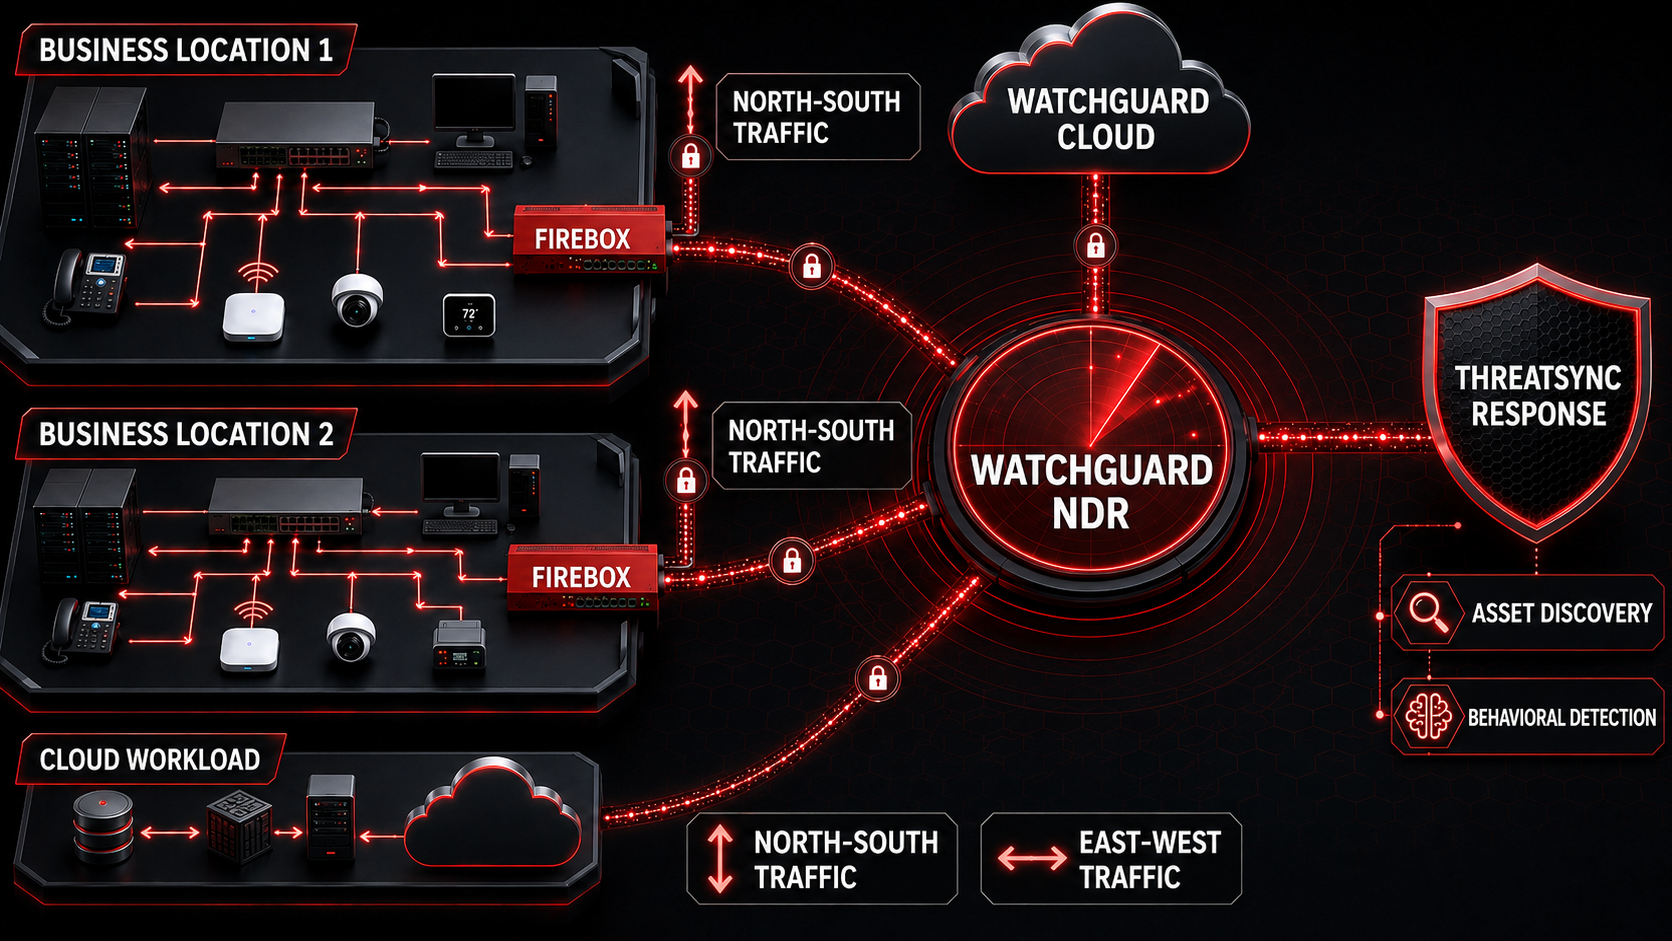
WatchGuard NDR applies AI and machine learning to network-flow data to uncover suspicious behavior across physical, private, cloud, and multivendor networks.
Why it matters
Attackers can move laterally between systems, communicate with command-and-control infrastructure, scan internal networks, or transfer data through devices that cannot run an endpoint agent. NDR continuously analyzes north-south and east-west traffic to expose those behaviors and prioritize action.
Choose the appropriate visibility
Coverage can begin with Firebox telemetry and expand to broader multivendor, cloud-workload, Microsoft 365, and compliance needs.
Behavioral detection and response based on network activity, VPN, and DHCP telemetry from supported Fireboxes.
Broader visibility using flow data from compatible switches, routers, firewalls, and supported cloud networks.
The broadest package, adding supported Microsoft 365 activity and expanded compliance reporting to network detection.
Core capabilities
Each capability addresses a specific part of the risk while sharing useful visibility with the broader WatchGuard ecosystem.
Flow-based machine learning identifies unusual access, beaconing, scanning, command-and-control activity, and suspicious data movement.
Internal traffic analysis helps reveal lateral movement and ransomware propagation that perimeter-only monitoring can miss.
Network observations identify subnets, important systems, unmanaged assets, and rogue devices, while supported Active Directory event collection adds user and group context to suspicious activity.
Supported Fireboxes provide telemetry directly, while collection agents can receive NetFlow or sFlow from compatible switches, routers, and third-party firewalls.
Smart Alerts, policy alerts, network threat scoring, and guided remediation help focus attention on the risks that matter most.
ThreatSync workflows can support actions such as blocking malicious addresses, isolating supported endpoints, or disabling compromised users.
The accountable layer
Technology becomes an operating security service when it is scoped, configured, monitored, maintained, and supported around the customer’s environment.
Business outcomes
Connected technologies
 ONE CONNECTED ECOSYSTEM
 Firebox
 Access Points
 ThreatSync XDR
 FireCloud Internet Access
 FireCloud
 Zero Trust Bundle
 Endpoint Security
 Endpoint Security Add-ons
 AuthPoint MFA
 Total Identity Security
 CloudDR
 Email Protection
 Patch Management
 Remote Monitoring & Management
 MDR Services
 Core MDR for Microsoft
 WatchGuard Cloud