24/7 monitoring
WatchGuard analysts continuously monitor supported Microsoft Defender for Endpoint signals rather than waiting for the customer to discover an alert.
 Start a conversation
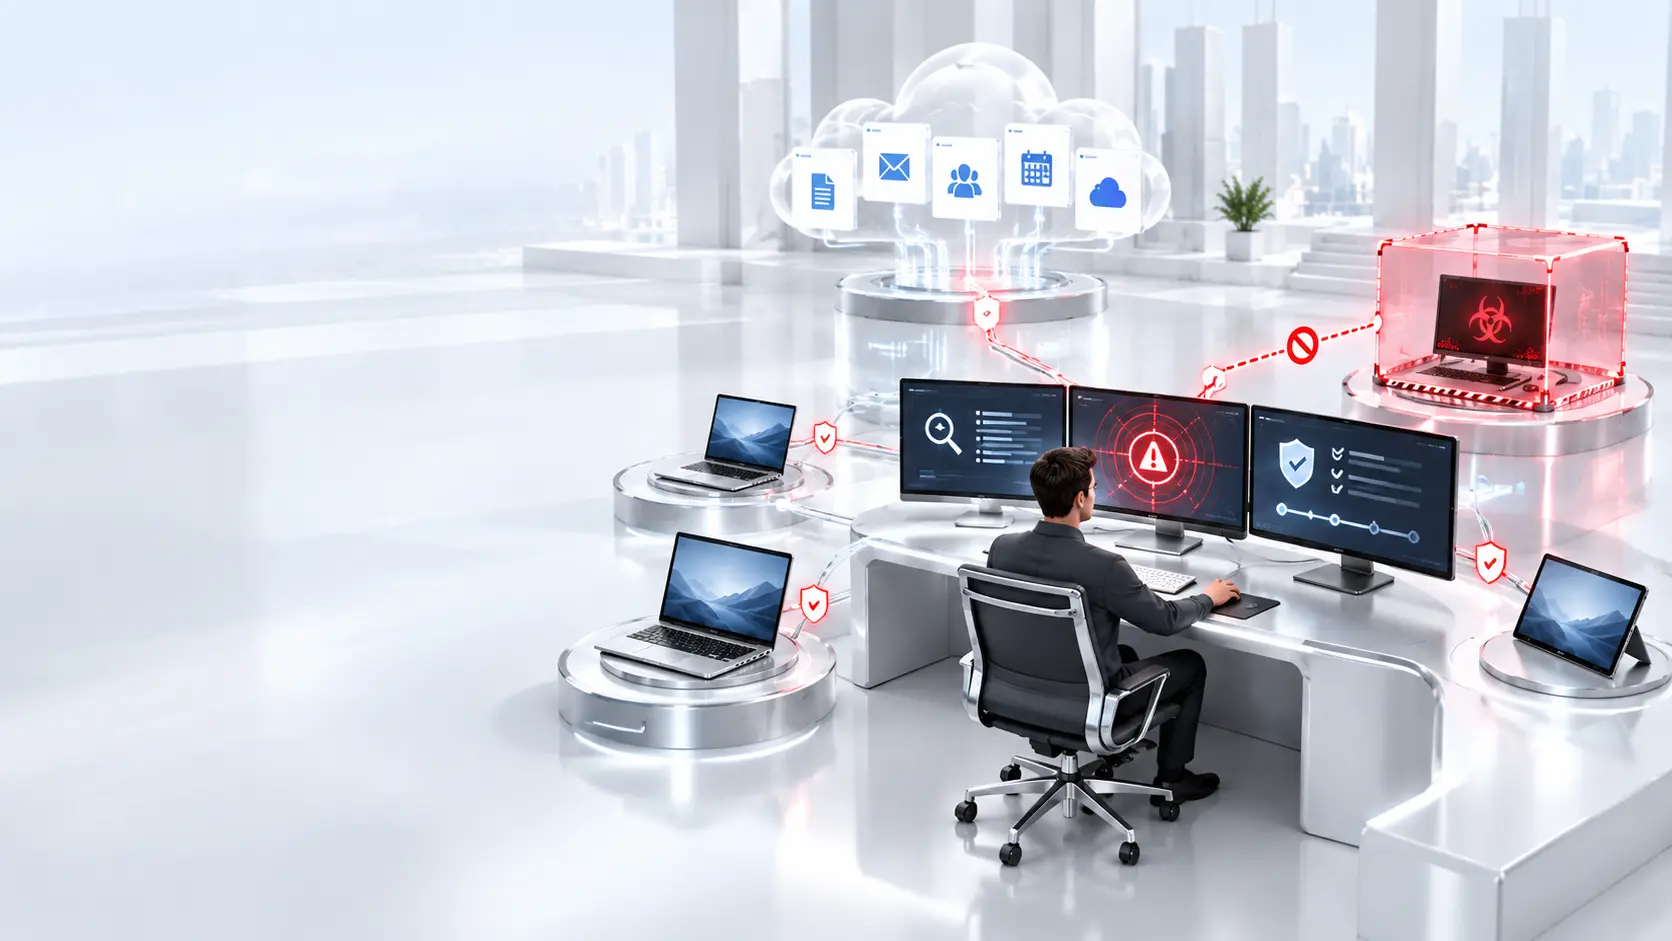
Managed response for Microsoft endpoints
WatchGuard Core MDR for Microsoft adds continuous expert monitoring, investigation, threat hunting, and response to supported endpoints protected by Microsoft Defender for Endpoint.
Why it matters
Many organizations own capable Microsoft endpoint protection but do not have a staffed security operations center. Core MDR for Microsoft gives those environments access to WatchGuard analysts who validate activity, investigate incidents, and coordinate or perform authorized response.
Core capabilities
Each capability addresses a specific part of the risk while sharing useful visibility with the broader WatchGuard ecosystem.
WatchGuard analysts continuously monitor supported Microsoft Defender for Endpoint signals rather than waiting for the customer to discover an alert.
Analysts validate suspicious activity, reduce false positives, determine scope, and assemble a clearer incident picture.
Proactive analysis searches for stealthy or developing threats that may not be obvious from an individual alert.
Supported containment and remediation actions help interrupt confirmed threats and limit further exposure.
Findings, affected assets, actions, and recommendations are documented for customer review and follow-up.
Kenmie remains the accountable partner for readiness, escalation, customer communication, and corrective work around the service.
Need broader WatchGuard telemetry?
Kenmie can use Core MDR for Microsoft where Defender is the endpoint foundation or Total MDR where the broader WatchGuard security ecosystem is in scope.
The accountable layer
Technology becomes an operating security service when it is scoped, configured, monitored, maintained, and supported around the customer’s environment.
Business outcomes
Connected technologies
 ONE CONNECTED ECOSYSTEM
 Firebox
 Network Detection & Response
 Access Points
 ThreatSync XDR
 FireCloud Internet Access
 FireCloud
 Zero Trust Bundle
 Endpoint Security
 Endpoint Security Add-ons
 AuthPoint MFA
 Total Identity Security
 CloudDR
 Email Protection
 Patch Management
 Remote Monitoring & Management
 MDR Services
 WatchGuard Cloud