Cross-domain correlation
ThreatSync XDR correlates supported network, endpoint, identity, and cloud activity so related security events can be investigated together.
 Start a conversation
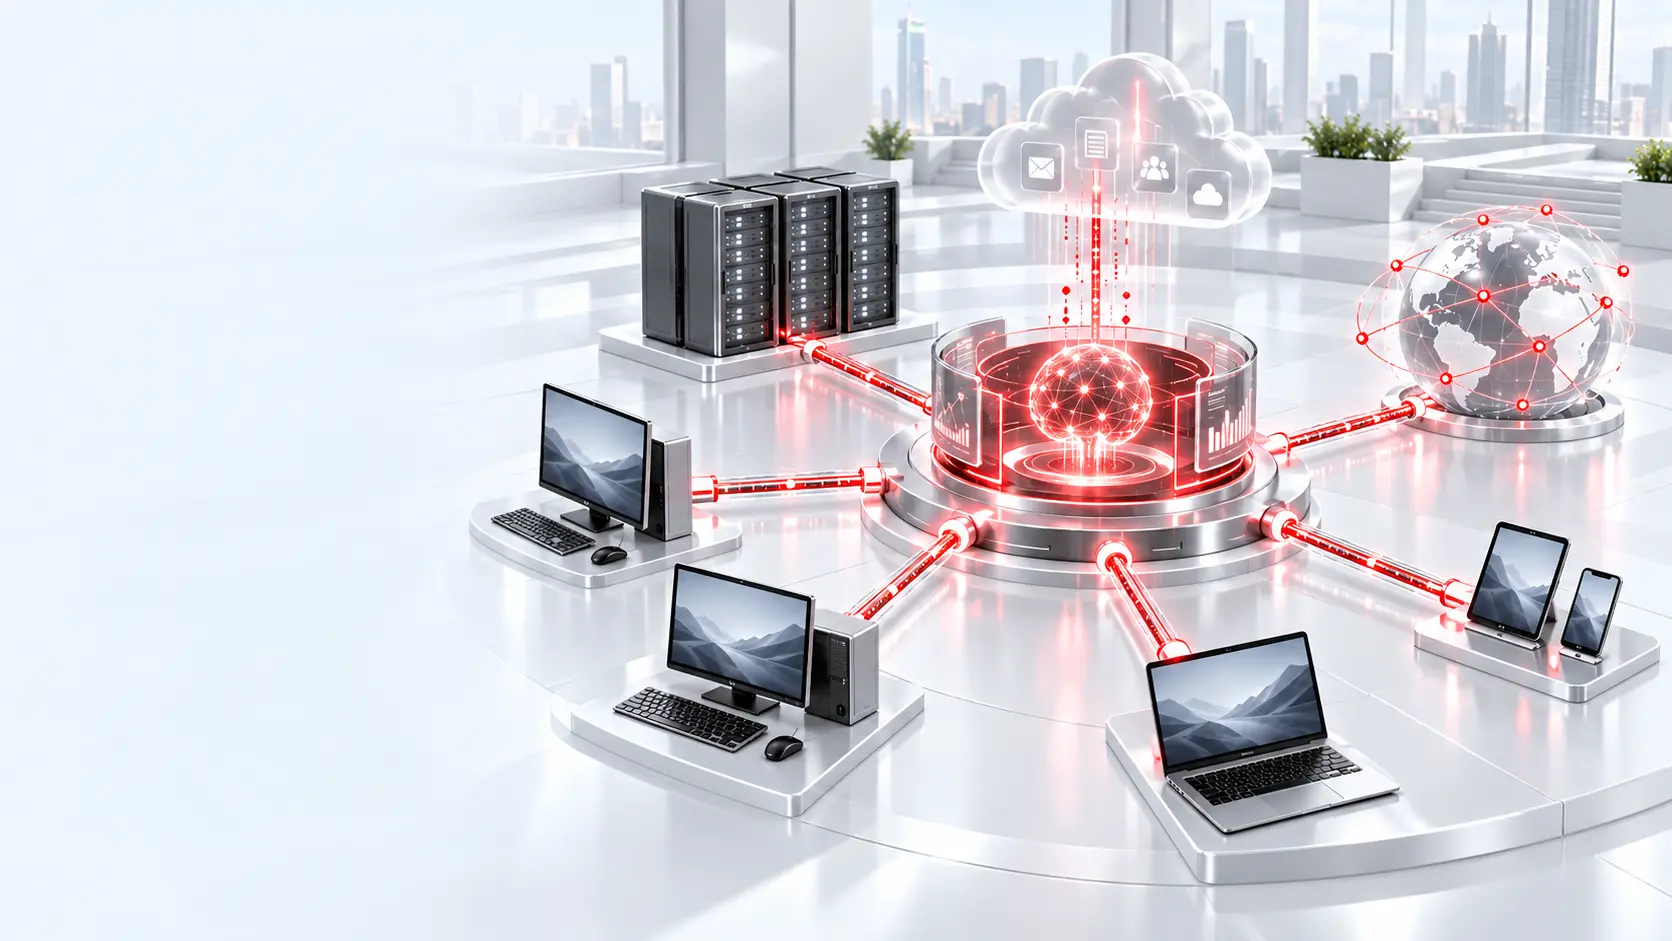
Correlate every signal
ThreatSync XDR correlates activity across supported WatchGuard security layers, reduces isolated alert noise, and helps responders prioritize and coordinate remediation through WatchGuard Cloud.
Why it matters
ThreatSync XDR connects those observations into a clearer incident picture. Cross-domain context, correlated alerts, and response workflows give Kenmie a more useful way to identify, investigate, and act on developing threats.
Core capabilities
Each capability addresses a specific part of the risk while sharing useful visibility with the broader WatchGuard ecosystem.
ThreatSync XDR correlates supported network, endpoint, identity, and cloud activity so related security events can be investigated together.
Related alerts are grouped and enriched with context so Kenmie can focus on activity that requires attention instead of isolated event volume.
A shared WatchGuard Cloud experience brings detections, affected assets, users, and response status into one operational view.
Supported actions can block malicious addresses, isolate endpoints, disable compromised users, and coordinate response across security layers.
Incident details help responders understand the sequence, scope, affected systems, and recommended next steps.
Organizations needing broader network, SaaS, and compliance visibility can extend the program with Total NDR.
Expand detection coverage
Total NDR combines WatchGuard NDR, WatchGuard SaaS, and Compliance Reporting in one coordinated package.
The accountable layer
Technology becomes an operating security service when it is scoped, configured, monitored, maintained, and supported around the customer’s environment.
Business outcomes
Connected technologies
 ONE CONNECTED ECOSYSTEM
 Firebox
 Network Detection & Response
 Access Points
 FireCloud Internet Access
 FireCloud
 Zero Trust Bundle
 Endpoint Security
 Endpoint Security Add-ons
 AuthPoint MFA
 Total Identity Security
 CloudDR
 Email Protection
 Patch Management
 Remote Monitoring & Management
 MDR Services
 Core MDR for Microsoft
 WatchGuard Cloud